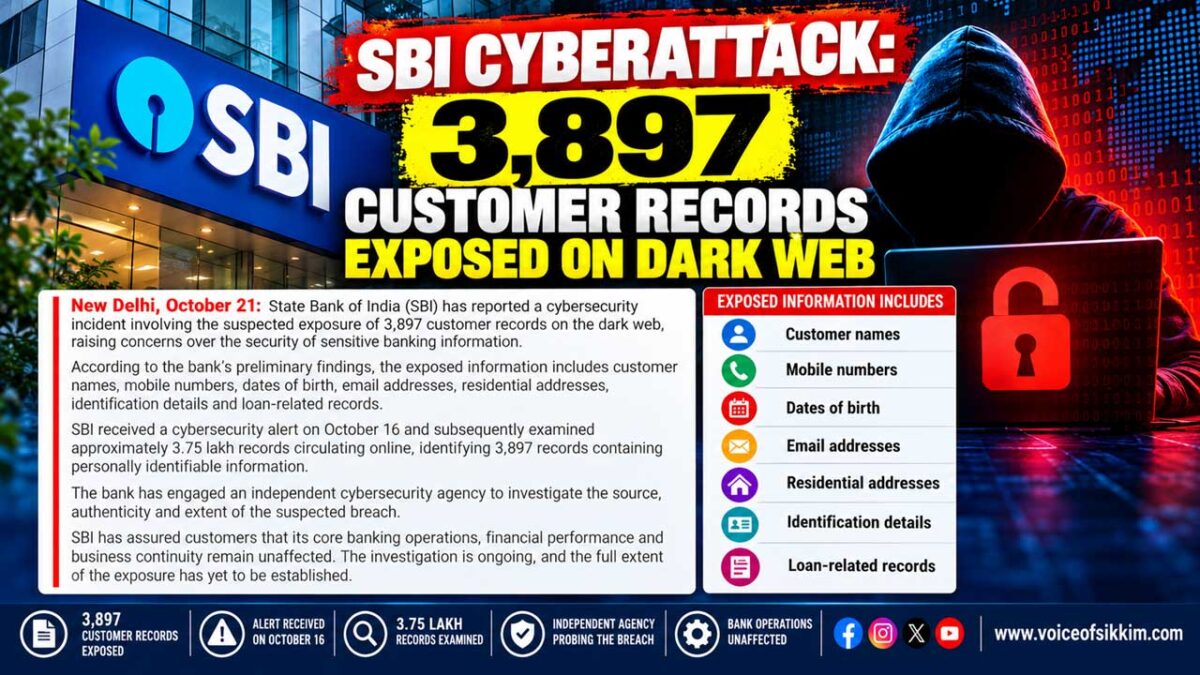
New Delhi, October 21, 2026: An SBI Cyberattack investigation has raised serious concerns over customer data security after the State Bank of India identified 3,897 customer records containing personally identifiable information among a much larger collection of records circulating on the dark web.
The suspected data exposure has prompted India’s largest public-sector bank to initiate an investigation into the origin and authenticity of the information, although the full circumstances surrounding the incident remain unclear.
Personal and Banking Information Exposed
According to the bank’s preliminary findings, the exposed records reportedly contain sensitive personal information, including customer names, mobile phone numbers, dates of birth, email addresses, residential addresses, identification details and loan-related information.
Such information can potentially be exploited by cybercriminals for identity theft, impersonation, phishing attacks and financial fraud.
However, the identification of customer information on the dark web does not, by itself, establish that SBI’s core banking systems were directly compromised.
Cybersecurity Alert Received on October 16
SBI reportedly received a cybersecurity alert on October 16, prompting an examination of approximately 3.75 lakh records circulating online.
During its preliminary assessment, the bank identified 3,897 records containing personally identifiable customer information.
The findings have raised questions about how the information became accessible and whether it originated from a direct security breach, a third-party system or another source.
The precise origin of the suspected exposure has not yet been established.
Independent Cybersecurity Investigation Ordered
Following the discovery, SBI engaged an independent cybersecurity agency to investigate the incident.
The investigation is expected to examine the authenticity of the exposed records, identify their possible source and determine the extent of any security compromise.
Further findings will be necessary to establish whether additional customer information was affected.
SBI Says Core Banking Operations Remain Unaffected
Despite concerns surrounding the suspected data exposure, SBI has maintained that its core banking operations, financial performance and business continuity remain unaffected.
The bank’s assurance indicates that the reported incident has not disrupted its regular banking services.
Nevertheless, the suspected exposure of personal information highlights the importance of protecting customer data in an increasingly digital banking environment.
What SBI Customers Should Know
Customers should remain cautious about suspicious calls, messages and emails claiming to originate from SBI.
Fraudsters may attempt to misuse personal information to impersonate banking officials or persuade customers to disclose confidential details.
Customers are advised never to share their OTPs, ATM PINs, passwords or banking credentials and to verify unusual communications through official SBI channels.
The investigation remains ongoing, and the complete extent of the suspected data exposure is yet to be determined.